External Penetration Testing Services

Approved by CREST

We run external penetration testing services that detect the internet-facing gaps a real attacker would find first: from exposed APIs to forgotten subdomains. You get proof that your systems can withstand an actual attack attempt, backed by evidence auditors and enterprise customers already trust. TechMagic is CREST-accredited and ISO 27001 certified, so every finding holds up under a compliance review or vendor assessment.

logo
logo
logo

Our Certificates

CREST Accreditation
CREST Security Testing - Penetration Testing
CompTIA CySA+ Cybersecurity Analyst certification badge
Our Certificates
Our Certificates
Our Certificates
eMAPT Mobile Application Penetration Tester certification badge
eWPT v1 eLearnSecurity Web Application Penetration Tester certification badge
Certified Network Security Practitioner certification badge by The SecOps Group
Our Certificates

What's Included in Your External Pentesting

List item image
Web applications and login portals

Your customer-facing web app, admin panel, and any authentication portal are the systems attackers reach first. We test them for logic flaws, broken access control, and cross-site scripting, so you know which one an outsider could actually walk through today.

List item image
VPN gateways and remote access systems

Your VPN (virtual private network) gateways and other remote-access systems sit at the edge of your external networks, between the open internet and everything behind your firewall. One misconfigured gateway can expose your whole internal network, and we tell you exactly which one before it becomes an incident.

List item image
Mail servers and email infrastructure

Your mail servers and email infrastructure stay a favorite target, since one compromised mailbox often unlocks password resets and a foothold for further security risks across your business. We test them the way a real attacker would, using manual techniques rather than a generic scan.

List item image
Exposed APIs and cloud-facing endpoints

Your APIs (application programming interfaces) and cloud-facing endpoints often carry more traffic than the web front end they support. We run vulnerability analysis on each one for broken authentication and excessive data exposure, so gaps surface before a customer or auditor finds them.

List item image
Subdomains and forgotten assets

Subdomains from an old campaign, a staging environment, or a project that shipped years ago rarely get decommissioned on schedule; along with shadow IT or other forgotten services a past team spun up, they follow the same pattern. Our external pen testing services find the ones still resolving and still answering requests from the open internet, because an attacker only needs one.

List item image
Network devices with public management interfaces

Routers, firewalls, and other network devices left with a management interface reachable from outside your firewall get tested against your existing security controls, since a default credential here can hand over your whole perimeter.

Our External Penetration Testing Methodology

Our External Penetration Testing Methodology

Step 1

Scoping and reconnaissance

Unlike internal pen testing, this engagement starts entirely from outside your network, with nothing but what's public. Before any active testing begins, we collect your target IP ranges, domains, and ASN data, then run passive OSINT: subdomain enumeration, Shodan and Censys scans, DNS reconnaissance, and checks for leaked credentials.

At this stage, we also agree on the testing model: black-box, where testers start with zero knowledge and simulate a full external attacker, or grey-box, where partial information speeds up coverage for a compliance-driven engagement.

Which model fits often comes down to your threat modeling priorities. Before a single test runs, we also lock in the scope document, the rules of engagement, which internet-facing systems are in play, any out-of-scope systems, and emergency escalation contacts.

Step 2

Attack surface mapping and exploitation

This is where reconnaissance turns into evidence. Asset discovery starts with active port scanning, service fingerprinting, and technology stack identification, and it's also where forgotten or shadow assets nobody remembered were still live tend to surface.

From there, vulnerability identification matches each discovered service version against known CVEs, checks for misconfigurations and weak authentication, and flags exposed admin panels and unpatched services that automated security tools alone tend to miss.

Exploitation comes next: we manually exploit each finding to prove practical impact, whether that means reaching sensitive data or gaining a foothold, and what it means for your business. To test what an attacker can reach once inside, we apply network penetration testing.

Finally, attack chain analysis ties individual vulnerabilities into a real exploit path, from initial access through privilege escalation to potential lateral movement risk into your internal networks. This is what a vulnerability scanner cannot show you.

Step 3

Reporting and debrief

You get three deliverables from every engagement, plus a live walkthrough. The executive summary is written for your CISO and C-level in plain language: the attack path narrative, a business risk summary, and the top remediation priorities, including what's at stake if an attacker reached your internal assets through this path.

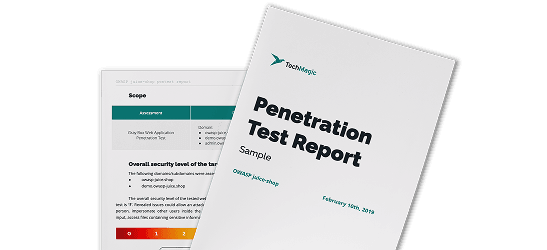
The technical report covers per-asset findings with CVSSv3 severity ratings (Critical, High, Moderate, or Low), proof-of-concept evidence, affected service details, and a remediation guide your developers can act on directly. The letter of attestation gives auditors, compliance reviewers, and enterprise partners the third-party proof they need that the test happened.

Then we debrief live: the tester who ran the engagement walks your security and engineering teams through the findings, explains each attack chain, and answers questions in real time.

Step 4

Remediation support and re-test

Once you've closed the findings, we re-test to confirm each fix holds, rather than just moving the same exposure one step closer to your internal systems. Re-testing is included as part of the engagement: we stay with you through remediation until every finding is verified closed.

Trusted by Teams That Put Security First

“TechMagic not only holds the CREST certification, but also went well above and beyond. Before we even scoped the project, they did extensive pre-work to understand our needs. They covered everything we required — code analysis, cloud infrastructure, even control protocols — working quickly and efficiently. I highly recommend TechMagic to any technical organization serious about security.”

A.J. Arango — VP of Security and acting Chief Information Officer at Corellium
Watch video
background
logo
Join Our 200+ Satisfied Clients

and leverage our industry-leading expertise to stay ahead of the curve in the fast-moving market landscape!

What External Penetration Testing Gives You Beyond a Vulnerability Discovery

What External Penetration Testing Gives You Beyond a Vulnerability Discovery

A tester's view of your internet-facing systems

An automated scanner just lists issues. Our pen testers show you which ones an attacker could actually chain together to gain access. They start with open source intelligence: what's publicly indexed, leaked, or exposed about your organization. Then, we work through the Penetration Testing Execution Standard (PTES): intelligence gathering, threat modeling, vulnerability analysis, exploitation, post-exploitation, and reporting. That structure surfaces the blind spots a scanner alone misses. It's narrower in scope than red teaming, which tests your whole organization over a longer engagement.

A clear picture of your real exposure

The test simulates the attacks a criminal group would actually try. They are often behind data breaches, denial-of-service incidents, and ransomware. You see how far an attacker could get before it costs you buyer trust or a legal bill. Those findings feed straight into your incident response planning, so your team knows what to watch for if something similar happens for real.

Security spend that goes where it matters

A planned assessment costs far less than cleaning up after a breach. Each external pen test gives you a prioritized view of where to put your security budget, weighed against your business objectives. Because the testing uses the same real-world tactics, that order reflects what an attacker would target first.

Evidence for your compliance requirements

Many industries require external penetration testing, and the report is how you document that you meet them. Teams that handle customer payment data often need it for PCI DSS. For frameworks like ISO 27001 or HIPAA, an external pen test is usually one required step on the way to a full audit pass.

Reputation protected before an incident goes public

We use established testing practices so you can close gaps quietly, before they disrupt operations or become a public incident. Many teams pair this with periodic red teaming to test the human side — a convincing phishing email can reveal gaps no firewall would catch. Fixing them ahead of time is more reliable and less costly than explaining a breach to customers after the fact.

Industries We Serve

Industries We Serve

FinTech

Our security specialists provide rigorous testing of online banking platforms, payment processing systems, financial applications, etc. We help FinTech companies protect against unauthorized access and data breaches.

Industries We Serve

MarTech

We help MarTech companies identify vulnerabilities in their web applications, databases, and customer management systems, ensuring that sensitive information remains secure.

Industries We Serve

HealthTech

Our penetration testing services are critical for HealthTech organizations to safeguard electronic health records (EHR), patient management systems, and telemedicine platforms. We help ensure compliance and protect patient privacy.

Industries We Serve

Your Industry

TechMagic's comprehensive external penetration tests are adaptable to the specific needs of any industry. Whether you operate in retail, education, government, or any other sector, we’ll be happy to help you identify and mitigate vulnerabilities, enhancing your overall security posture.

Our Team

Ihor Sasovets
Ihor Sasovets
Lead Security Engineer

Ihor is a certified security specialist with experience in penetration testing, security testing automation, cloud and mobile security. OWASP API Security Top 10 (2019) contributor. OWASP member since 2018.
CompTIA PenTest+ certification badge
Certified AppSec Practitioner certification badge by The SecOps Group
AWS Certified Security – Specialty certification badge
AWS Certified Cloud Practitioner certification badge
eWPT v1 eLearnSecurity Web Application Penetration Tester certification badge
Certified Cloud Security Practitioner – AWS certification badge by The SecOps Group
Blue Team Level 1 Tester certification badge
eJPT Junior Penetration Tester certification badge
Certified Mobile Pentester – Android certification badge by The SecOps Group
EC-Council Certified Ethical Hacker (CEH) certification badge
eMAPT Mobile Application Penetration Tester certification badge
Certified Cloud Pentesting Expert – AWS certification badge by The SecOps Group
Certified AI/ML Pentester certification badge by The SecOps Group
Roman Kolodiy
Roman Kolodiy
Director of Cloud & Cybersecurity

Roman is an AWS Expert at TechMagic. Helps teams to improve system reliability, optimise testing efforts, speed up release cycles & build confidence in product quality.
AWS Certified Security – Specialty certification badge
Project Management Professional (PMP) certification badge
AWS Certified DevOps Engineer – Professional certification badge
Victoria Shutenko
Victoria Shutenko
Security Engineer

Victoria is a certified security specialist with a background in penetration testing, security testing automation, AWS cloud. Eager for enhancing software security posture and AWS solutions
Name=C-AgAIPen gray.png
eMAPT Mobile Application Penetration Tester certification badge
AWS Certified Cloud Practitioner certification badge
Certified AppSec Practitioner certification badge by The SecOps Group
Certified Cloud Security Practitioner – AWS certification badge by The SecOps Group
eJPT Junior Penetration Tester certification badge
eWPT v1 eLearnSecurity Web Application Penetration Tester certification badge
Certified AI/ML Pentester certification badge by The SecOps Group
eWPTX eLearnSecurity Web Application Penetration Tester eXtreme certification badge
Certified Mobile Pentester – Android certification badge by The SecOps Group
Certified Network Pentester certification badge by The SecOps Group
Certified Network Security Practitioner certification badge by The SecOps Group
|

Discover Our Featured Case

In-depth VPN server pentest for 
a software development company

In-depth VPN server pentest for a software development company

See how we helped Blackbird enhance the security of their VPN server infrastructure

Orest Kutiuk
icon

To ensure the security of existing functionality TechMagic provided BlackBird with security testing service, including one Black Box VPN Server pentest in accordance with best practices, PTES, OWASP testing guide, and Penetration testing methodologies. The team's project management was effective and fast. They delivered the project adhering to strict deadlines and expected outcomes. Their professionalism and transparency were impressive.

Orest Kutiuk

Technical Project Manager, BlackBird Lab

Conducting a pentest for a Danish software development company

Conducting a pentest for a Danish software development company

See how we helped Coach Solutions improve the security of their web application

Theis Kvist Kristensen
icon

“TechMagic has great collaboration and teamwork. Also a good proactive approach to the task.Everything went as planned and on time.”

Theis Kvist Kristensen

CTO COACH SOLUTIONS

Why Choose TechMagic

Expertise and certified security professionals

Our security team has extensive experience detecting and exploiting vulnerabilities, proven by PenTest+, CEH, eJPT, eWPT, and AWS Security Specialty certifications. We stay updated with the latest attack methods to provide comprehensive testing tailored to your specific needs.

001

/003

Security and compliance

002

/003

Proven track record and reliability

003

/003

FAQs

Let’s safeguard your project
Ross Kurhanskyi
Ross Kurhanskyi

VP of business development

linkedin-icon

Trusted by:

logo
logo
logo
logo
cookie

We use cookies to personalize content and ads, to provide social media features and to analyze our traffic. Check our privacy policy to learn more about how we process your personal data.