
 Software Development
 Security Services
 Cloud Services
 AI Services
 Other Services





 TechMagic Academy


ISO 27001 Consulting Services
ISO 27001 preparation becomes manageable when you know exactly what to focus on. Our ISO 27001 consultants help you define scope, map controls, close documentation and operational gaps, and organize audit-ready evidence. Get a reliable process that builds a clear path to certification.

We're Trusted by





It’s often unclear what should be in the ISMS scope: which systems, data flows, and vendors should be included to meet ISO 27001 requirements. Deciding what’s “good enough” is rarely straightforward, and ISO wording is easy to misinterpret without guidance from experienced ISO 27001 consultants.
Policies may look complete on paper, but daily practices rarely follow them. In reality, teams apply IAM, logging, change management, and vendor oversight inconsistently across systems. These mismatches create clear gaps that auditors spot immediately.
Collecting audit-ready evidence often takes longer and requires more coordination than expected. Each control requires documentation, ownership, and validation, which means teams must constantly track where artifacts live and if they're up to date. Without a defined process, Security, Engineering, IT, HR, and Operations quickly fall out of sync.
Our ISO 27001 Services Build a Reliable, Audit-Ready ISMS
Case Studies Demonstrate Our ISO 27001 Consulting Expertise
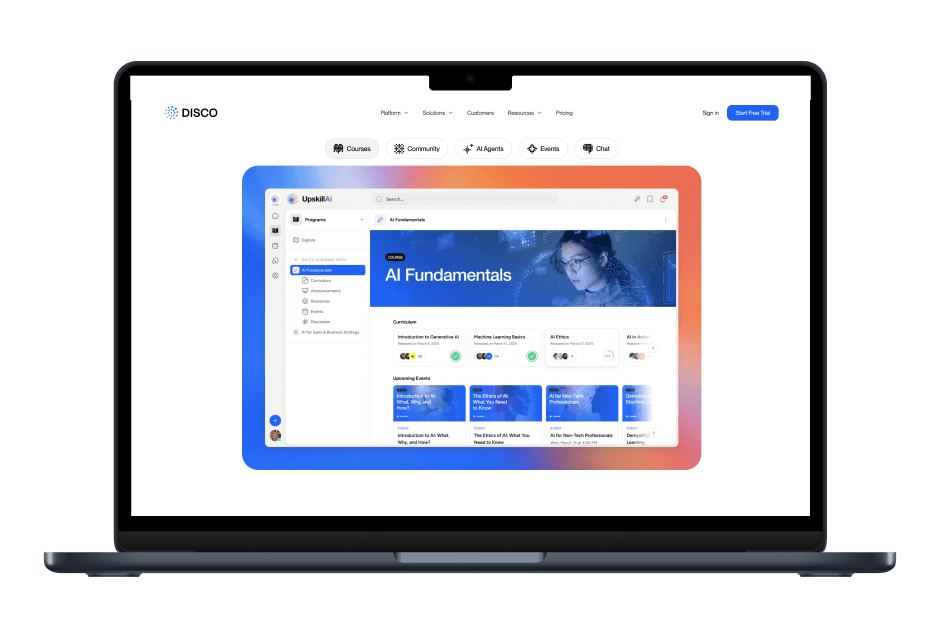
TechMagic helped Disco achieve FERPA compliance through a structured gap assessment, data privacy governance design, and an institution-ready documentation framework
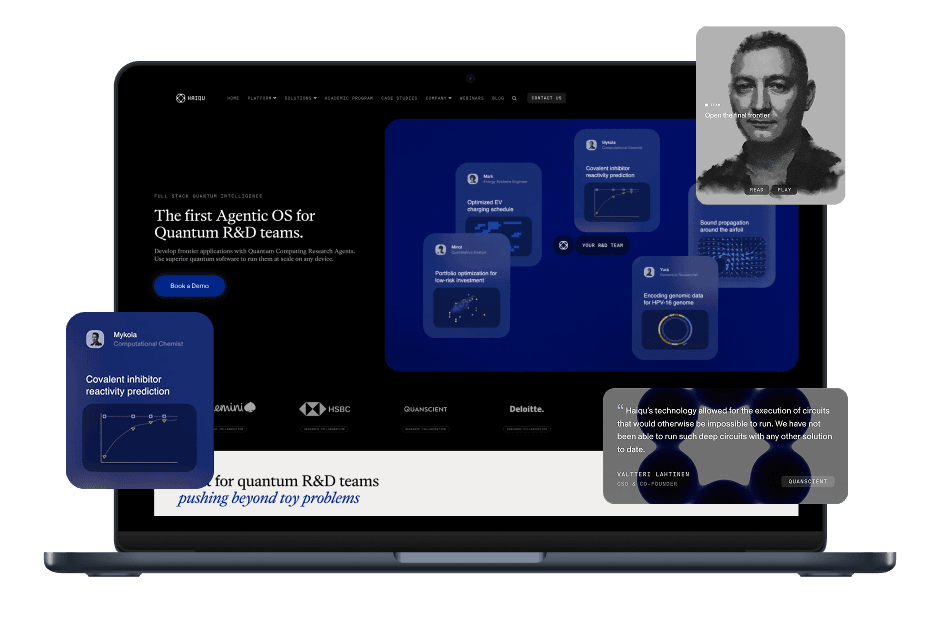
TechMagic built a full security program for Haiqu, a quantum computing platform, guiding it to ISO/IEC 27001 certification, validating it with CREST-accredited penetration testing, and hardening its cloud environment, all under one partnership.
Check how we helped Quizrr conduct an internal security audit, prepare for ISO 27001, and strengthen customer trust.

TechMagic helped Disco achieve FERPA compliance through a structured gap assessment, data privacy governance design, and an institution-ready documentation framework
TechMagic built a full security program for Haiqu, a quantum computing platform, guiding it to ISO/IEC 27001 certification, validating it with CREST-accredited penetration testing, and hardening its cloud environment, all under one partnership.
The most exposed areas in FinTech are the flows that handle financial data and identity. FinTech products process payments, account data, and banking integrations, which require strict access governance and strong transaction integrity. We help companies secure API communication, apply encryption, and strengthen vendor risk oversight, a common weakness during ISO 27001 certification consulting for financial systems.
The biggest vulnerability of HealthTech platforms is their reliance on many interconnected systems. They store PHI and exchange data with EHRs, labs, and insurers. Integrations demand secure data flows and reliable authentication. We refine audit logging around clinical events and set clear retention rules. We also align workflows with HIPAA and similar regulations that intersect with ISO 27001 requirements.
Cloud and hosting providers manage high-value systems where small misconfigurations create major risk. We clarify the shared responsibility model and strengthen IAM at every layer. Our ISO 27001 implementation consulting improves monitoring and logging coverage. We also simplify evidence collection across distributed environments.
SaaS teams must prove security maturity to win enterprise deals. Multi-tenant access control is often the first concern. We tighten environment separation and guide change management in fast release cycles. Our ISO 27001 certification consultancy for SaaS companies also helps improve customer data isolation and create incident response steps that match real operational behavior.
Service firms handle client data, credentials, and intellectual property on a daily basis. We standardize device management and secure data exchange across projects. As an experienced ISO 27001 consulting company, we document delivery workflows to reduce ambiguity. We also improve vendor oversight so engagements stay consistent and audit-ready.
You Get Benefits That Strengthen Security and Business

We Guide you Through Every Stage of ISO 27001 Preparation

Why Choose TechMagic
TechMagic’s ISO 27001 consultants work with industries that face strict security expectations, such as SaaS, FinTech, HealthTech, and cloud services, applying in-depth knowledge. We map ISO controls to real workflows and avoid template-driven approaches. Our experts in ISO 27001 consultancy services align the ISMS with regulatory and contractual requirements and verify that controls produce reliable audit evidence.
001
/003
002
/003
003
/003
Let’s safeguard your project
VP of business development

Trusted by:


FAQs

Security
15 min read
Security
19 min read
Security
9 min read
Security
15 min read

Security
20 min read
Security
9 min read
