
 Software Development
 Security Services
 Cloud Services
 AI Services
 Other Services





 TechMagic Academy


SOC 2 Compliance Consulting Services
When nonadherence to SOC 2 becomes a blocker for deals, partnerships, or growth, TechMagic helps you address it with focused, practical SOC 2 compliance consulting. We start with a clear gap analysis, strengthen existing controls, and guide evidence gathering step by step. Through this approach, we help you reduce security risk, protect client data, and enter the audit knowing your systems are ready.

We're Trusted by





Our SOC 2 Services Support You Throughout the Journey
Security and Compliance Outcomes We've Delivered for Clients
Check how we helped Quizrr conduct an internal security audit, prepare for ISO 27001, and strengthen customer trust.

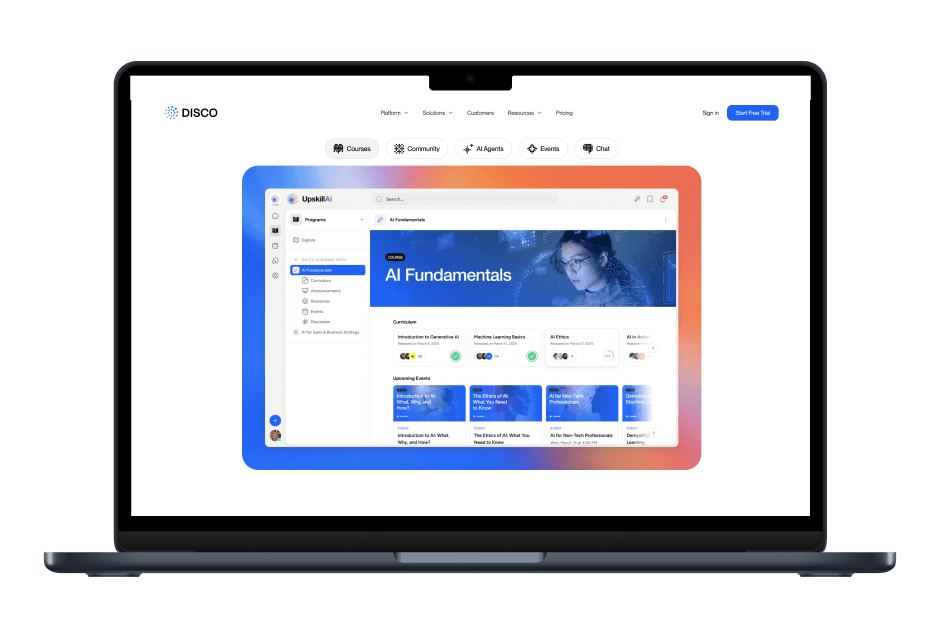
TechMagic helped Disco achieve FERPA compliance through a structured gap assessment, data privacy governance design, and an institution-ready documentation framework
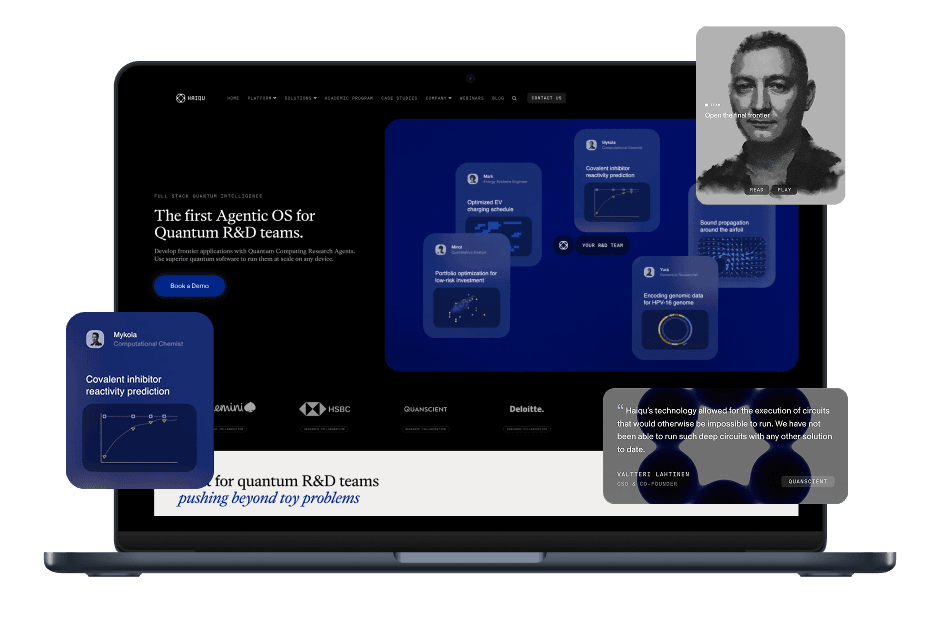
TechMagic built a full security program for Haiqu, a quantum computing platform, guiding it to ISO/IEC 27001 certification, validating it with CREST-accredited penetration testing, and hardening its cloud environment, all under one partnership.
Check how we helped Quizrr conduct an internal security audit, prepare for ISO 27001, and strengthen customer trust.
TechMagic helped Disco achieve FERPA compliance through a structured gap assessment, data privacy governance design, and an institution-ready documentation framework
We're Certified Security Professionals


TechMagic Prepares You for Both SOC 2 Audit Types
SOC2 Type I Audit Preparation
SOC 2 Type I focuses on whether your controls are designed correctly at a specific point in time. It’s often the first formal step for teams that need to show early progress to clients, investors, or partners.
As a SOC 2 audit consultant, we help you prepare for this milestone. To make this happen, we review your current controls, identify gaps, and align policies and processes with audit expectations. We guide your teams to make sure controls are clearly defined, documented, and ready for review. The goal is not just to pass the audit, but to establish a solid foundation that strengthens your security posture and sets you up for Type II.

SOC 2 Type II Audit Preparation
SOC 2 Type II evaluates how well your controls operate over a defined period, typically 6 months or more. This is where many teams struggle: not with design, but with consistency, evidence, and ongoing execution.
We support teams throughout the entire observation period. In particular, we help operationalize controls, monitor how they perform in real conditions, and prepare structured evidence that shows controls working as intended over time. Our SOC 2 compliance consultant services aim to reduce audit stress, surface issues early, and help you achieve compliance without disrupting daily operations or delivery cycles.

We Help Different Industries Achieve SOC 2 Readiness
In FinTech, companies handle highly sensitive financial data and must meet strict regulatory requirements. Our SOC 2 compliance consulting helps secure system access, maintain integrity in financial reporting, and prevent fraud. We guide teams to ensure their data handling processes meet industry standards. This includes providing clear documentation and controls that satisfy financial institutions, investors, and partners. By doing this, we help FinTech companies maintain high security without slowing down growth.
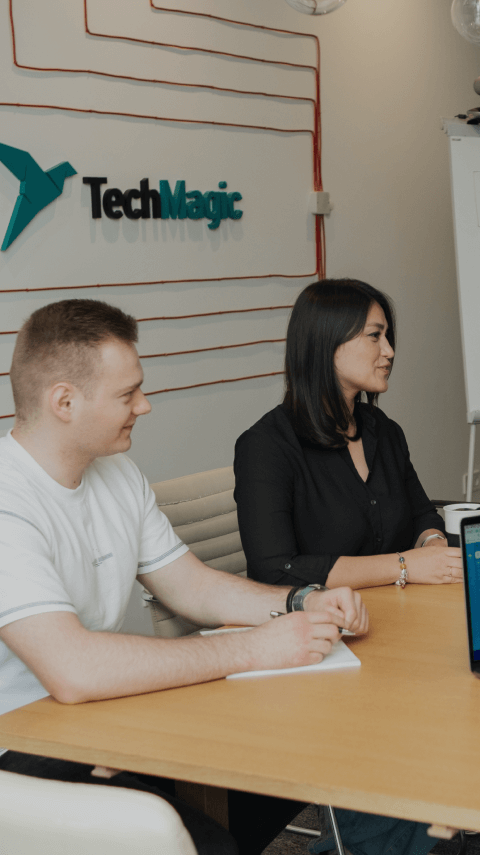
HealthTech companies handle personal health information, which requires robust protection under health data regulations. We assist teams in strengthening patient data security while ensuring systems remain available. Our SOC 2 security consulting helps organizations establish controls to protect sensitive data and comply with healthcare industry regulations. The goal is to help HealthTech companies prove that their systems operate securely and consistently while we reduce risks and ensure compliance.
Cloud and infrastructure services face high expectations around availability, security, and resilience. We help these organizations implement and maintain controls to ensure infrastructure security and protect client data. Through evidence gathering and proving the effectiveness of security frameworks, we make sure cloud providers can present reliable SOC 2 reports. This is essential for clients who need to trust that your systems are secure, resilient, and compliant, no matter how your infrastructure evolves.
For SaaS companies, SOC 2 is a crucial requirement as businesses scale. Clients need greater assurances about data security. To meet these expectations, we ensure your security controls are well-integrated across multi-tenant platforms, user access, and continuous monitoring. We help teams align security practices with real product behavior. This way, you can provide audit-ready evidence without disrupting your development cycle. Whether expanding services or attracting new clients, we support in meeting SOC 2 requirements efficiently.
Technology and IT service providers manage complex systems across internal teams, customer environments, and third-party vendors. Our SOC 2 compliance services help organizations define clear ownership of data security responsibilities. We ensure that each part of your system meets the required security standards. We support accurate system descriptions and ensure controls work effectively across your infrastructure. This approach helps prevent breaches and safeguards customer data in complex IT environments.
Our SOC 2 Audit Consulting Process Is Clear and Structured

Why TechMagic
Dedicated quality and security testing practices support everything we deliver. As a trusted partner, we validate controls, workflows, and system behavior not through assumptions but with structured reviews and security testing. Our SOC 2 security consulting focuses on how controls perform in real conditions, across infrastructure, applications, and access management, so issues surface early.
001
/003
002
/003
003
/003
Let’s safeguard your project
VP of business development

Trusted by:


FAQs
Explore Our Trending Publications
Security
9 min read

Security
20 min read
Security
17 min read
Security
11 min read
Security
FinTech
14 min read

Security
15 min read
