



How TechMagic Achieved ISO 42001 Certification
TechMagic achieved ISO/IEC 42001 certification in September 2026. In about three months, our information security experts built an AI management system (AIMS) that governs how employees use AI tools in daily work. The AIMS extends our existing ISO 27001 and ISO 9001 processes instead of running as a separate system.
Software development and IT consulting
ISO/IEC 42001:2023
~3 months (June-September 2026)
About the Certification Scope
TechMagic provides custom software development, IT consulting, and software development outsourcing and outstaffing services, which form the scope of its ISO/IEC 42001 certificate. We already held ISO 27001 and ISO 9001 certifications and ran an integrated management system (IMS) built on both standards. For this certification, we defined our role as an AI user: the AIMS governs how we select, approve, and use AI tools from third-party vendors.
AI tools are part of our everyday work, and the AIMS covers all of them. Developers use AI coding assistants and AI-powered IDEs, while marketing uses AI for content, presentations, images, and training videos. Other departments work with general-purpose AI assistants, AI search, workflow automation, and AI features in data platforms.
Beyond software development, we help clients prepare for compliance frameworks such as ISO 27001, SOC 2 and FERPA. ISO 42001 is a new standard, so we wanted to go through certification ourselves before guiding clients through it.
Context and Starting Point
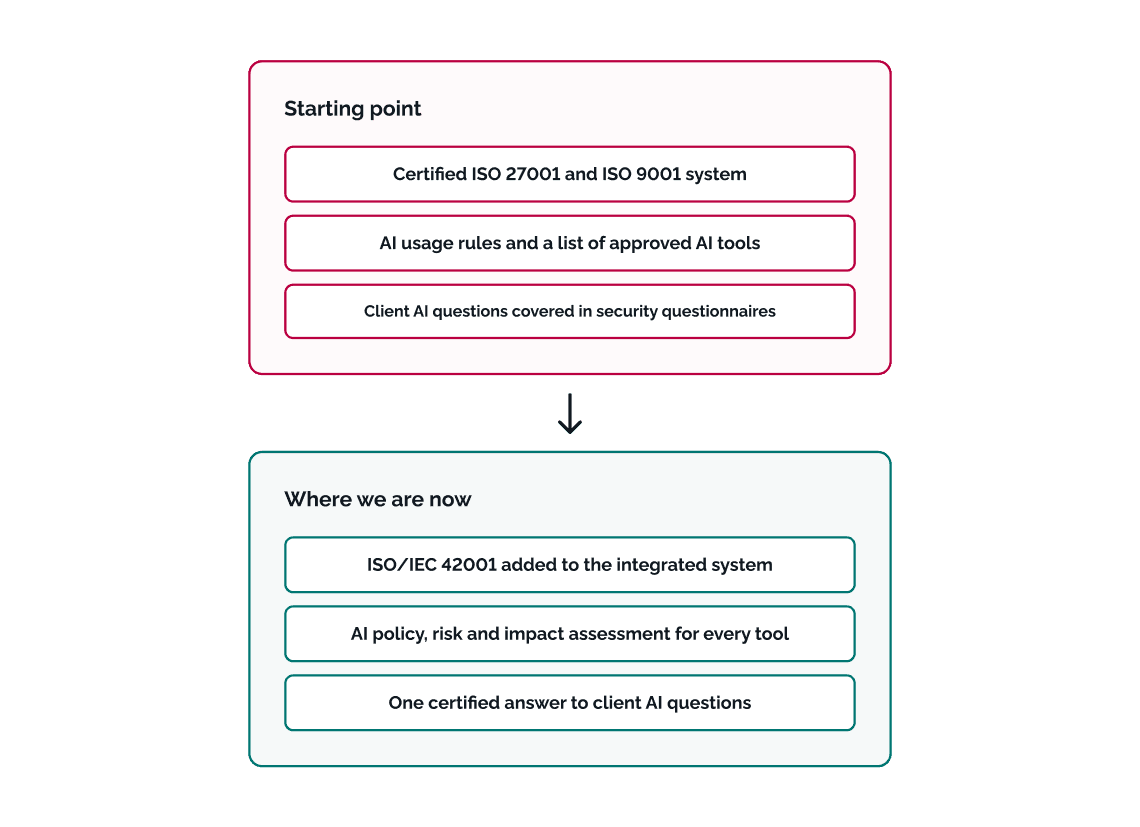
TechMagic needed a clear answer to a question clients had started to ask: how do its employees use AI? Security questionnaires asked which tools employees use, what data goes into them, and how the output is reviewed. These questions needed a governance answer beyond ISO 27001. Growing internal use of third-party AI models and the EU AI Act’s push for documented governance added weight. We chose ISO/IEC 42001 certification as a long-term answer instead of handling each questionnaire case by case. We already had basic AI usage rules and a list of approved AI tools. The next step was to turn them into a managed system with an AI policy, clear governance roles, a risk assessment for each tool, and a process to assess how AI tools may affect people. The system also had to fit the way we work: AI tools are in daily use, and the controls could not slow down software delivery.
What Made Our ISO 42001 Certification Process Different
Our information security experts designed and implemented the system, so objectivity had to be built in from day one. One consultant led the architecture, another handled implementation, and management approved every policy.
The AIMS joined an IMS that already covered ISO 9001 and ISO 27001. The work meant extending proven processes to AI instead of creating parallel ones.
The scope covered every AI tool in use, grouped into five categories and used by developers, sales, recruitment, marketing, and other departments.
“Our clients started asking how our team uses AI: which tools, what data goes into them, and how the output is checked. We decided to answer that with a certified management system instead of one questionnaire at a time. Because we built it on our existing ISO 27001 and ISO 9001 processes, AI governance didn’t become extra bureaucracy; it became part of how we already work.”
Information Security Manager
How We Prepared for ISO 42001 Certification, Stage by Stage
TechMagic prepared for ISO/IEC 42001 in about three months by extending its integrated management system to AI. Some stages ran in parallel.
Key Implementation Challenges and Solutions
The most demanding part of the project was applying ISO/IEC 42001 controls to everyday AI use. Each issue needed a clear decision and a documented reason.

As an AI user, we had to decide which Annex A controls applied. Data controls were first excluded, although they also covered the data employees entered into AI tools.

We kept the data controls in scope for data entered into AI tools. All nine controls for the AI system life cycle (Annex A.6) were marked not applicable, as development and deployment of third-party AI tools are the vendors’ responsibility. The final Statement of Applicability marks 27 of the 38 Annex A controls as applicable.
A full impact assessment for every AI tool would have taken weeks, and much of that effort would have gone to tools with little effect on people.
We introduced a four-question screening as the first step. A full assessment now follows only when a tool may affect people, so the effort goes where it matters.
Some AI tools process personal data, so they needed closer attention than tools used for code or content.
We required a full impact assessment for these tools and introduced human review of their AI-generated output.
New rules for AI use could have added approval steps to software development and slowed down project delivery.
AI-generated code already went through code review, so we added no new approval steps to development. Engineers use approved tools with defined data rules and complete AI onboarding before access. The rollout caused no significant pushback or slowdown.
ISO 42001 Certification Readiness Deliverables
The project produced the documents and processes that now form TechMagic’s AIMS.
The AIMS Scope Policy sets the boundaries of the management system and describes the context it works in.
The AI Policy sets company-wide rules for responsible AI use, and AIMS Performance Measurement defines KPIs for AI objectives.
The AIMS Governance Policy defines who is responsible for each part of the system.
The AI Inventory Register records each AI tool with its risk rating, allowed data classification level, and mandatory settings.
The AIMS Risk Management Procedure assesses AI with the same method and levels used for information security.
The AIMS Impact Assessment Procedure and the AIIA Register document how AI tools may affect people.
The Statement of Applicability records which Annex A controls apply and why.
The AI Tool Management Process covers tool requests, vendor checks, approval, onboarding, and offboarding.
The AI Resources Process and the Information Classification Policy define what data may be entered into AI tools.
The Supplier Relationships Management Policy covers AI vendors as suppliers.
The LMS course “AI at Work: Practical Tips for Responsible Use” is part of onboarding under the HR Security Policy, and HR keeps the training records.
A joint internal audit report covers ISO 9001, ISO 27001, and ISO/IEC 42001, and management reviews are recorded.


Questions about internal AI use now get one documented, audited answer instead of case-by-case explanations.

Corporate licenses for AI coding tools replaced reimbursed personal subscriptions, and access starts only after AI onboarding.

AI-generated code goes through the standard code review, so project delivery keeps its usual pace.
SOC 2 compliance preparation and ISO consulting are a core part of our work, alongside FERPA and other frameworks. Our consultants hold credentials such as ISO 27001 Lead Auditor, CISSP and CISM. For example, our vCISO service helped Haiqu, a quantum computing platform, build its ISMS and achieve ISO 27001 certification in about three months. ISO 42001 audit preparation is the newest addition to this practice.
We went through scoping, risk and impact assessment, internal audit, and the certification audit for our own AIMS. That experience shows where the effort goes and which decisions matter most. One lesson: auditors expect a named person responsible for AI governance, so we help clients assign one at the start.
We extend existing ISO 27001 processes to AI instead of building a separate system, so much of the groundwork is already in place. A short screening decides which tools need a full impact assessment, and AI controls fit into routines such as onboarding and tool requests.
Let’s safeguard your project
VP of business development

Trusted by: